Trust
A protected environment is not defined only by encryption. It is defined by what remains visible, chosen and governed by the user.
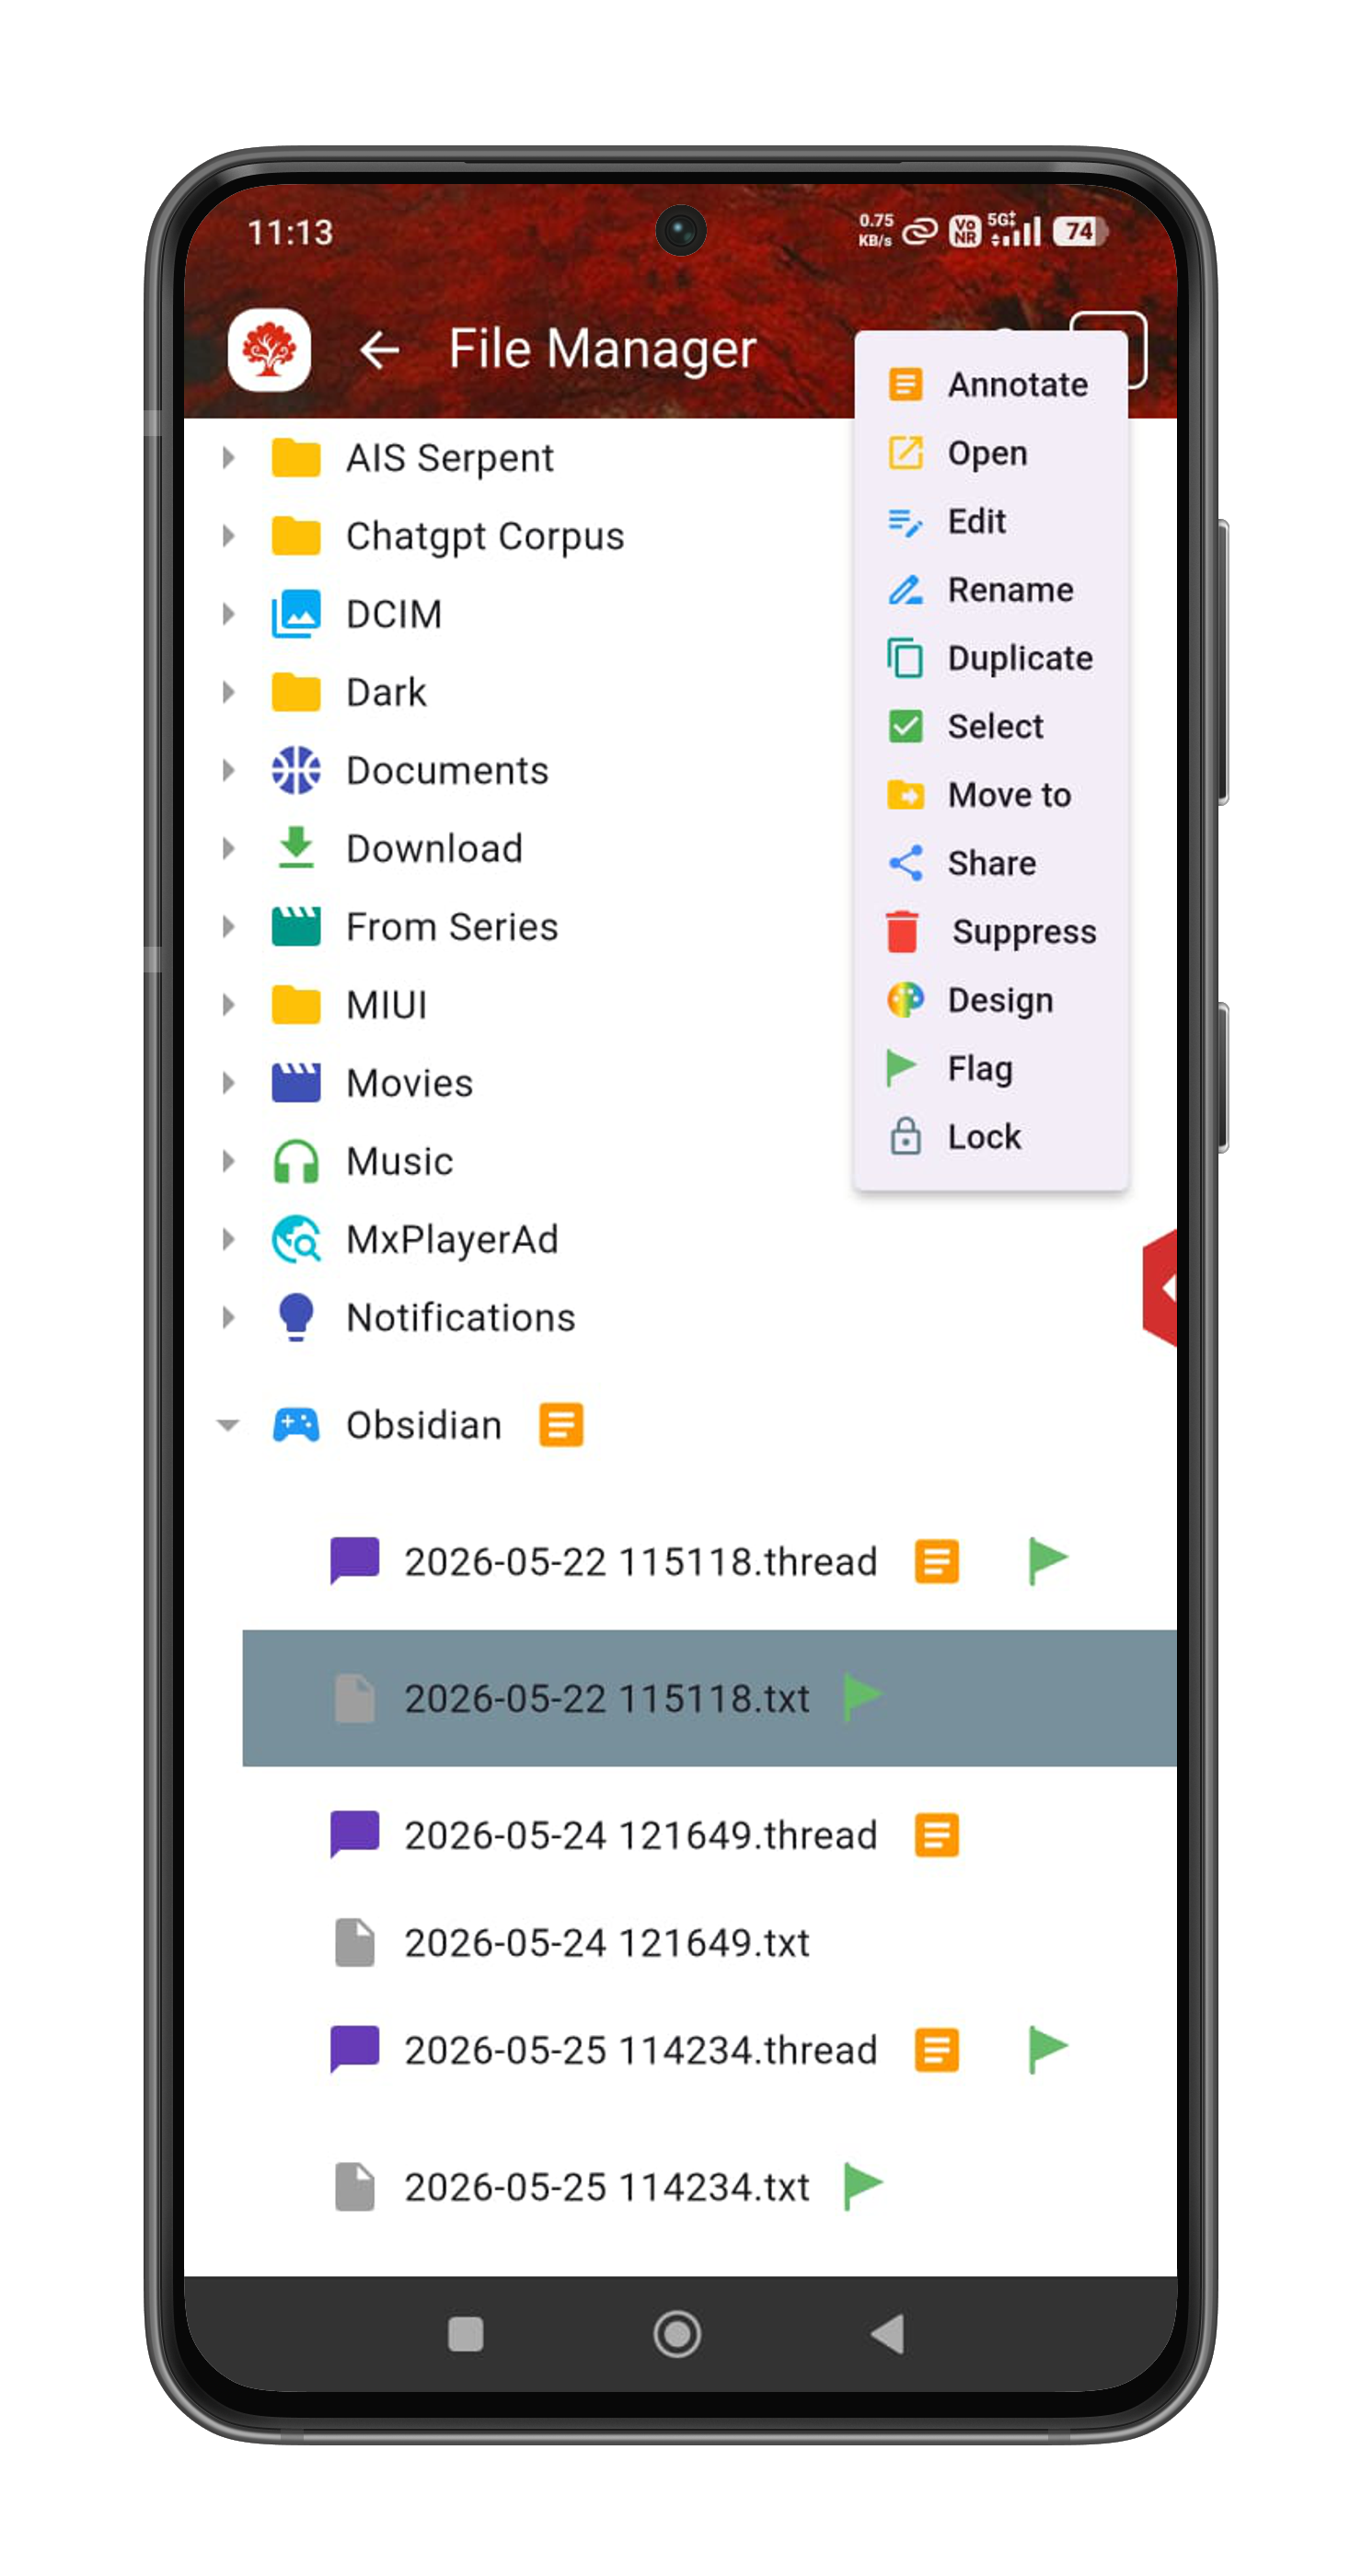
Nothing is shared without an explicit decision.
The user determines what enters a connected service, what an artificial system may examine, and what another person may access.
RedTree can begin locally and extend through synchronized services without making the local environment secondary.
Backup status, synchronization scope and active sharing remain inspectable from the environment itself.
Artificial systems operate from selected context and within explicit limits. Assistance does not become silent authority.
Operational security, hosting, retention and recovery disclosures will be published with the production release.
